Without trust, data cannot create value
Without trust, data cannot create value.
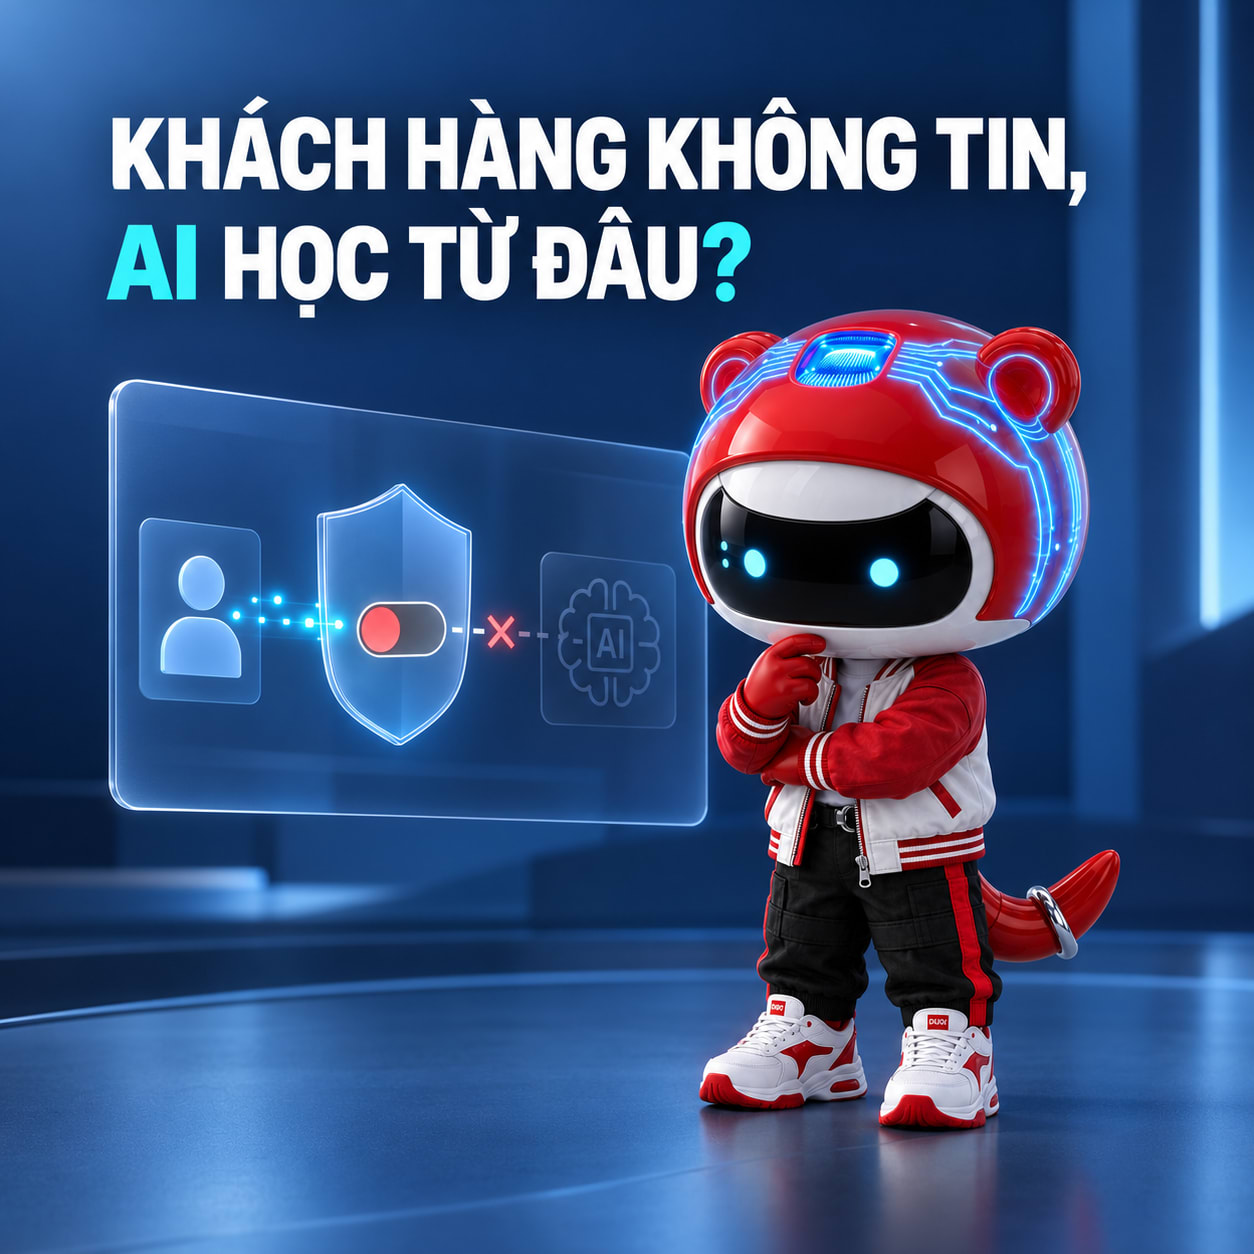
Businesses may possess a strong data platform and a good AI model, but as soon as customers stop sharing data, all that advantage begins to erode. Trust, therefore, is not a communication issue; it is a component of the technology architecture.
The UK's health innovation minister has expressed concern that a lack of trust in Palantir could affect the willingness to share data with the NHS. Between mid-May and mid-July 2026, approximately 60,000 more people withdrew access to their data for research and planning. This withdrawal did not affect data directly used in treatment. (The Guardian)
There isn't enough data to conclude that all the withdrawals originated from Palantir. But the event highlights an important issue: the value of a data platform depends not only on technology, but also on whether users continue to allow the system to use their data.
DUDI Software's Perspective
The key issue isn't a specific vendor or technology contract. The bigger problem is that businesses often view customer consent as a checkbox on a form, when in reality it's a data state that can change throughout the customer journey.
Customers may agree to provide information to complete a transaction but not consent to the use of that data for marketing. They might allow data analysis to improve service, and then later reverse their decision.
If the website, CRM, data warehouse, and AI systems fail to update to these changes, the business may continue to use data outside the permitted scope.
A good compliance system doesn't just know whether a customer has agreed or not. The system must know for what purpose they agreed, when, through which channel, and which version of the policy is applied.
Websites are where trust begins.
Most data-sharing decisions are made on websites or apps. This is also where businesses are most likely to erode trust.
A long form, vague wording, or pre-enabled options might boost consent rates in the short term. But customers will struggle to understand what their data is being used for, who it's being shared with, and how they can withdraw it.
Designing a privacy-focused experience shouldn't stop at a cookie window. Websites need to clearly separate purposes such as service operation, analytics, personalization, and marketing. These choices must be clear enough for users to make informed decisions without having to read a lengthy legal document.
Withdrawing consent should be as simple as giving it. If customers have to send an email, call a hotline, or wait for staff to process their request manually, businesses are turning data control into an opaque process.
CRM must manage both data access rights and other data access permissions.
CRM systems typically store contact information, transaction history, and purchase behavior. However, not all data within a CRM can be used for every purpose.
Businesses need a consent record linked to each customer. When a customer changes their choice on the website, the status in the CRM must be updated. The marketing, customer service, and analytics systems must also receive the corresponding changes.
If a customer has withdrawn their permissions but is still receiving personalized content based on their past history, the problem isn't just a wrongly sent email. It indicates that systems are using different versions of the same person's permissions.
ERP and internal processes must be able to implement customer decisions.
Data can be copied from the CRM to a data warehouse, management reports, ERP, or partner systems. Therefore, updating a field in the CRM is not enough to guarantee that customer rights are protected.
Businesses need to know where data originates, which systems it resides in, and which processes it's being used for. When access rights change, the system must be able to restrict processing, stop synchronization, or exclude data from a specific task.
This is why data governance cannot be left solely to the legal department. Regulations must be translated into operational logic that software can execute and verify.
The more data-driven AI becomes, the more important trust becomes.
AI requires sufficiently large, accurate, and representative data. When many people withdraw their access, the dataset can shrink or become unbalanced. The results of analysis and forecasting therefore risk becoming less reliable.
Businesses shouldn't grant AI access to all data simply because the system has connectivity capabilities. Each task needs to be granted the necessary scope. Sensitive data should be minimized, masked, or aggregated whenever possible.
More importantly, businesses must be able to demonstrate what data was used, for what purpose, and which provider processed it. Without the ability to trace data, businesses will find it very difficult to explain when customers ask questions.
What preparations do businesses need to make?
- Manage consent as data with a clear history, purpose, and timeframe.
- Connecting the state of user access rights between the website, CRM, ERP, marketing, and AI systems.
- Evaluating providers is based on access control, access logs, retention time, and the ability to discontinue data use.
Data only becomes an asset when customers believe that the business is using it for the right purposes. For sustainable AI development, businesses must invest simultaneously in technology, data governance, and trust protection mechanisms.